

A continuous vulnerability scanner that maps every finding to the SOC 2, ISO 27001 and PCI DSS control it breaks
Visit cyberspec.pro ↗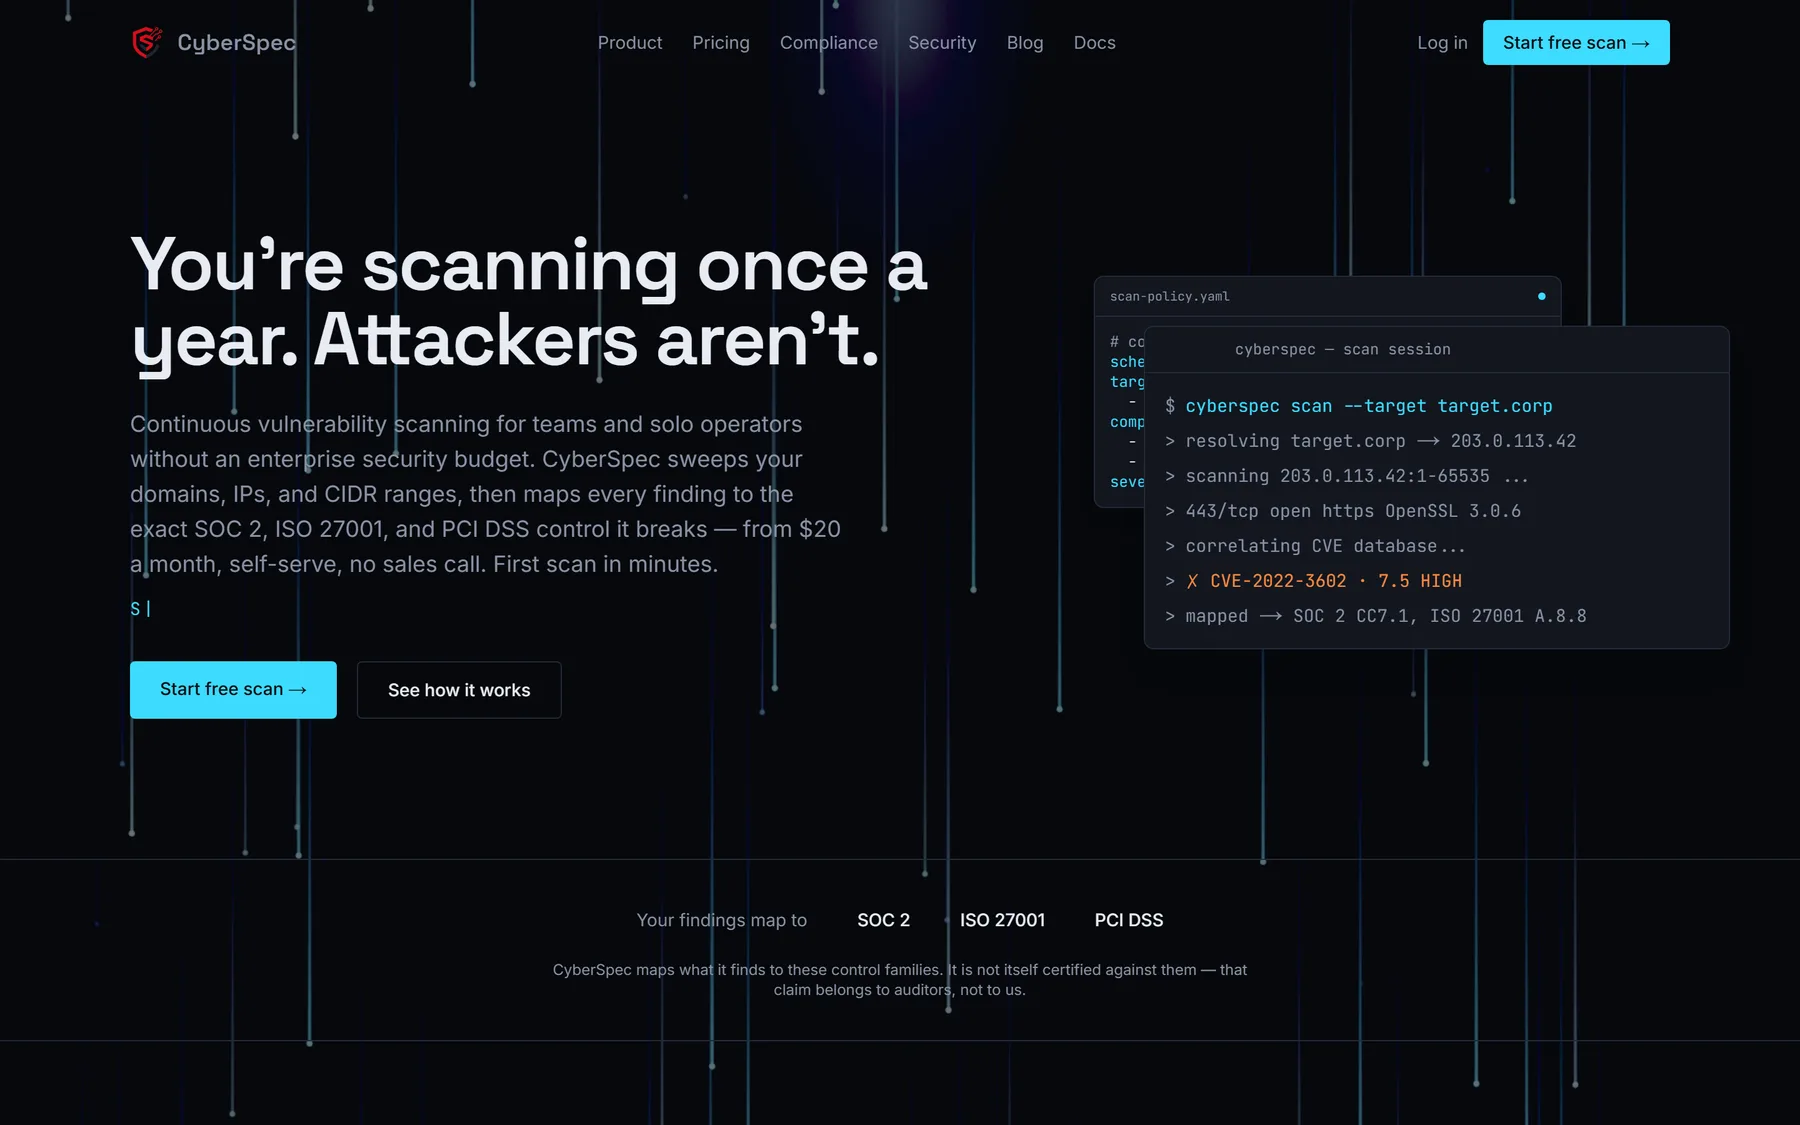
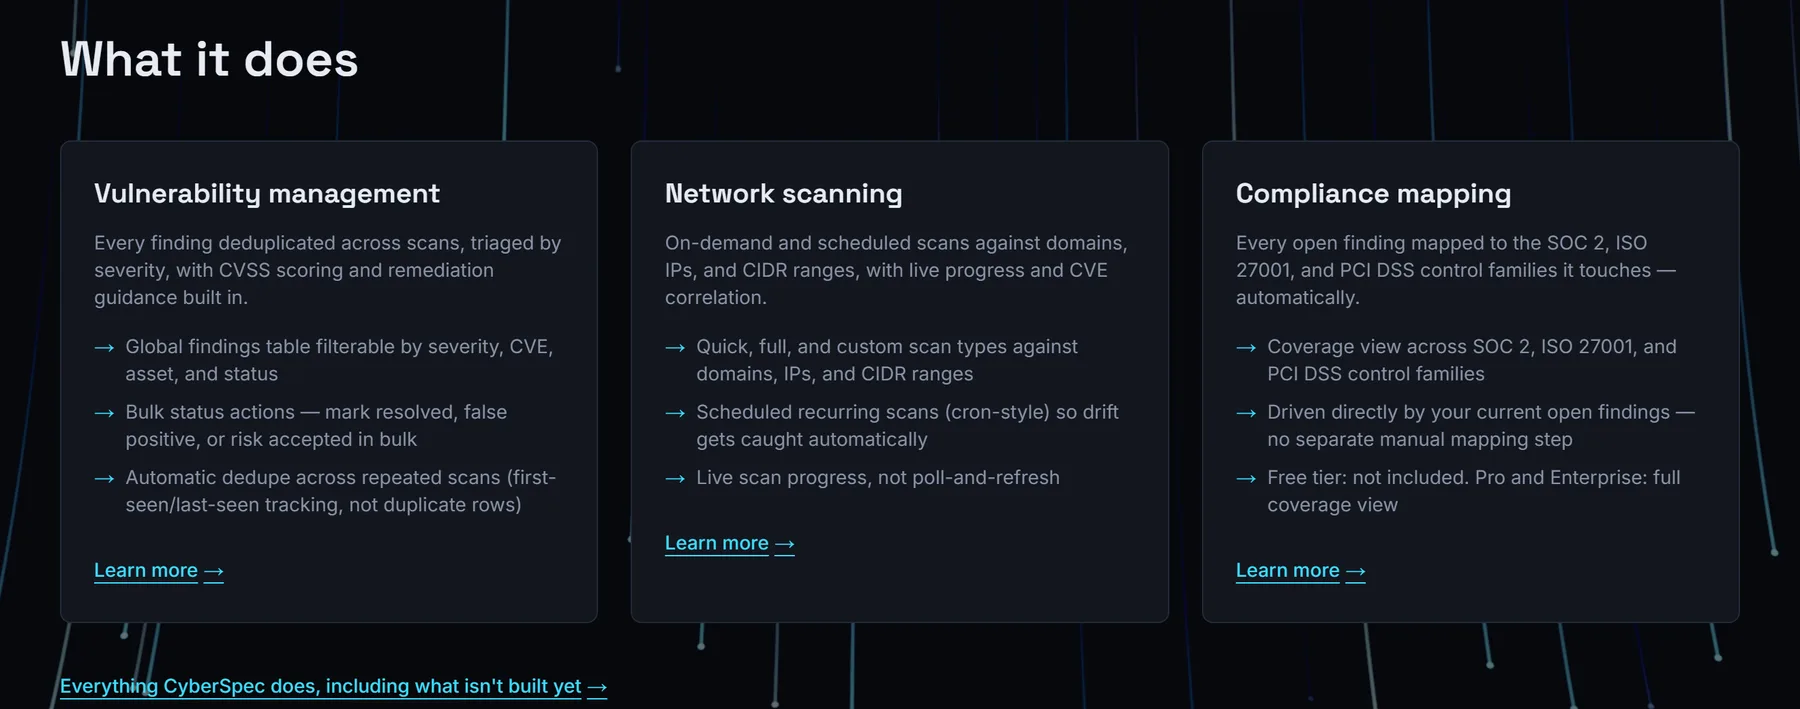
- Scheduled scans across domains, IPs and CIDR ranges
- CVE correlation with CVSS scoring and remediation guidance
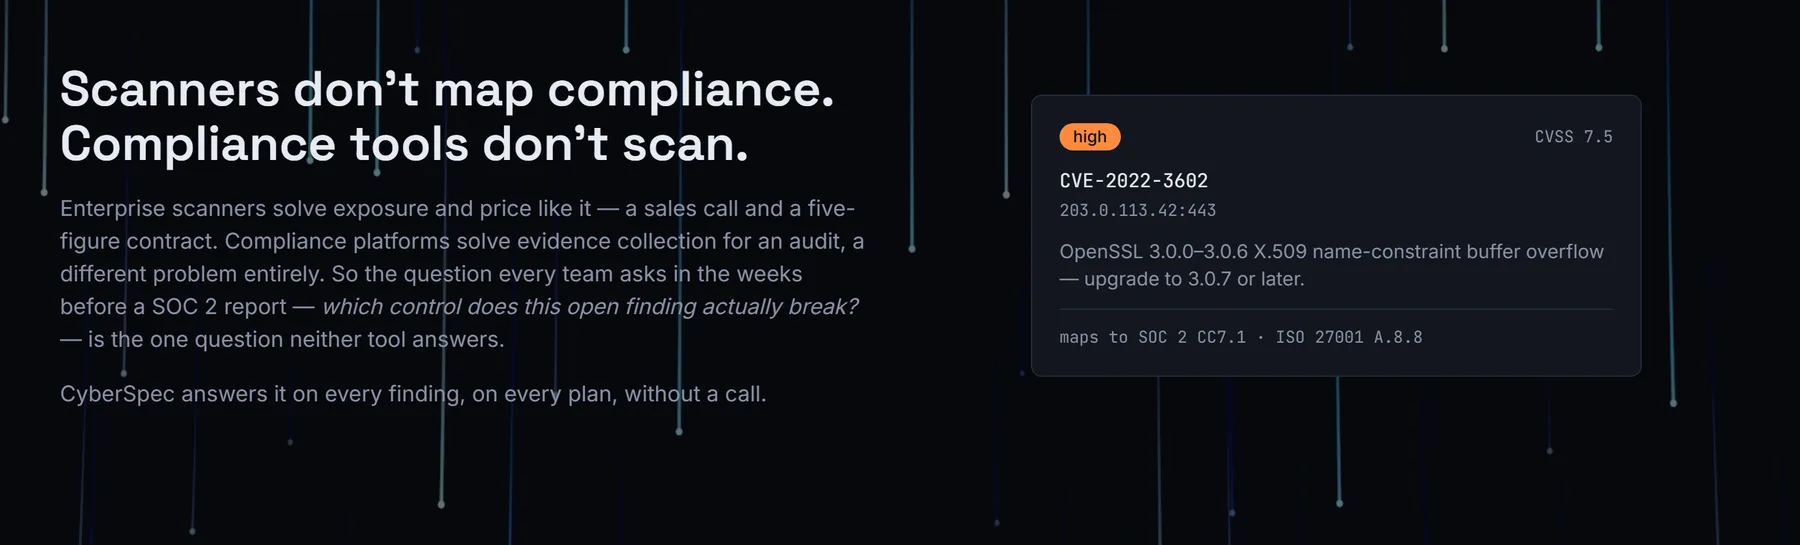
- Automatic mapping to SOC 2, ISO 27001 and PCI DSS controls
- Findings deduplicated across scans with first/last-seen tracking
- YAML scan policies and an API for CI/CD
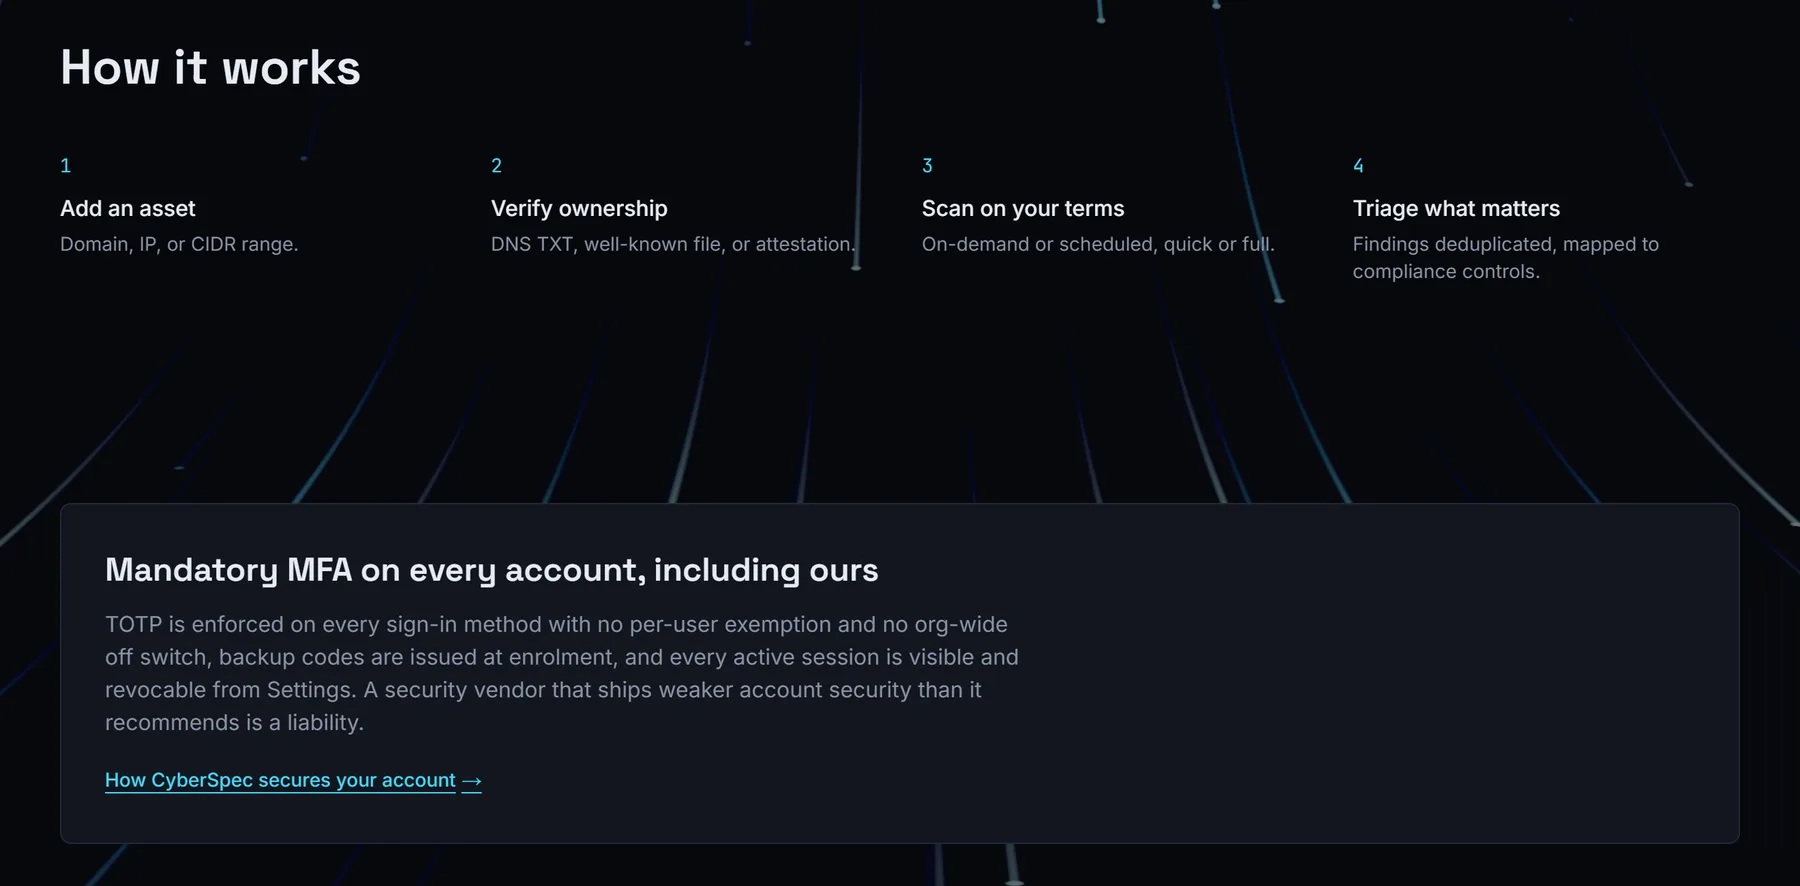
- Mandatory TOTP MFA on every account, no exemptions
The problem
Enterprise scanners find exposures but open at five figures and a sales call. Compliance platforms collect audit evidence but don't scan anything. In the weeks before a SOC 2 report, every team asks the same question — which control does this open finding actually break? — and neither kind of tool answers it. Small teams were left scanning once a year while attackers scan constantly.
The approach
We designed and built CyberSpec as one product that does both jobs. Users add a domain, IP or CIDR range, prove ownership by DNS TXT record, well-known file or attestation, then scan on demand or on a cron-style schedule with live progress. Every result is correlated against the CVE database, scored by CVSS, deduplicated across runs with first-seen and last-seen tracking, and mapped automatically to SOC 2, ISO 27001 and PCI DSS control families. Scan policies are plain YAML and the API plugs into CI/CD. Because it is a security product, it holds itself to its own standard: TOTP MFA is mandatory on every account, with no per-user exemption and no org-wide off switch.
The outcome
CyberSpec is live and self-serve at cyberspec.pro, with a free tier (one asset, no card) and a $20/month Pro plan covering 20 assets, scheduled scans and full compliance mapping. A team can go from sign-up to first scan in minutes, and every open finding arrives already tied to the audit control it affects.
Inside CyberSpec.
Facing a similar problem?
Tell us what you're building — we'll tell you honestly whether we're the right fit.
Talk to us